Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
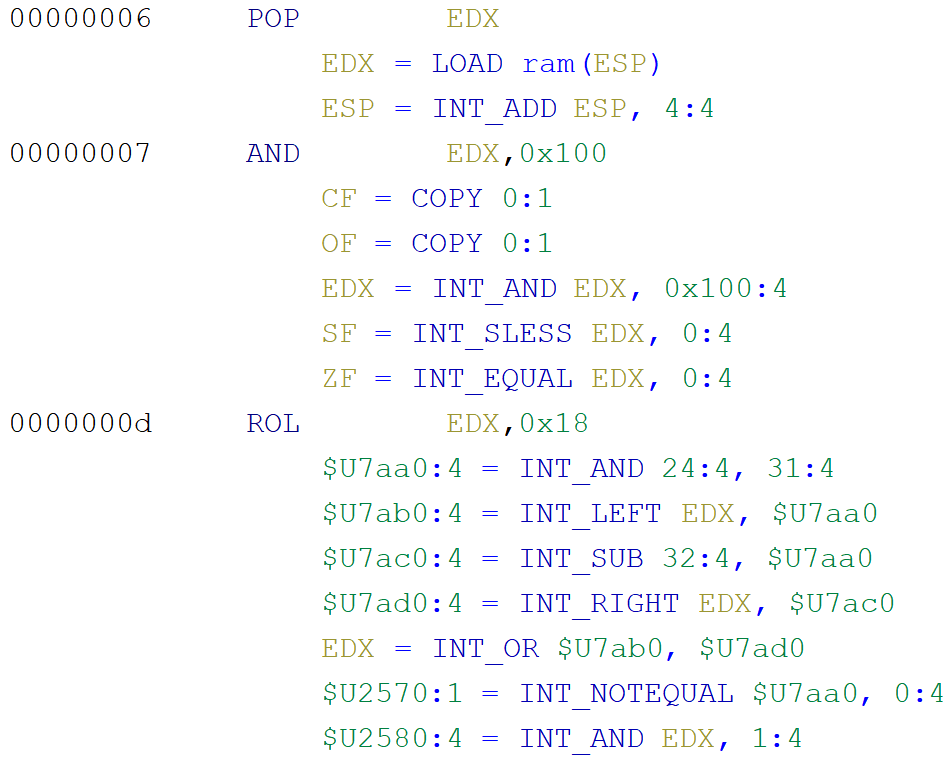
Example of aliasing in Ghidra. While Ghidra finds the cpu flags ...
Part 2: Reverse Engineering and Patching with Ghidra | Coalfire
How to train your Ghidra | Securelist
Comment Utiliser Ghidra _ Ghidra Free Download – DFXDX
Reverse Engineering with Ghidra
Пример реверс инжиниринга с использованием Ghidra
how to infer data type in ghidra decompilation result - Reverse ...
Ghidrathon | Snaking Ghidra with Python 3 Scripting | Mandiant | Google ...
Guide: Ghidra Tutorial - Decompiling | HSI
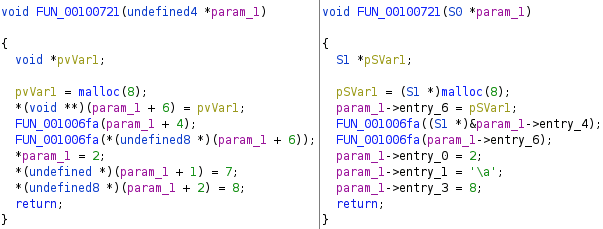
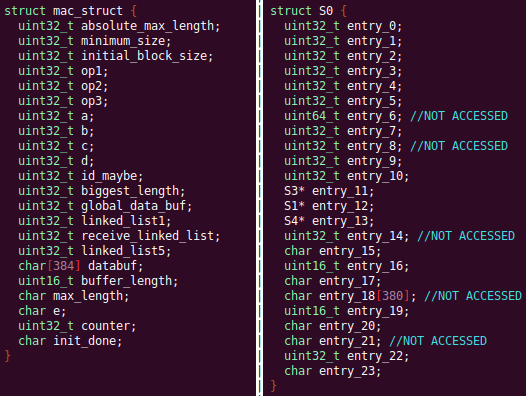
Automated Struct Identification with Ghidra | GRIMM Cyber R&D
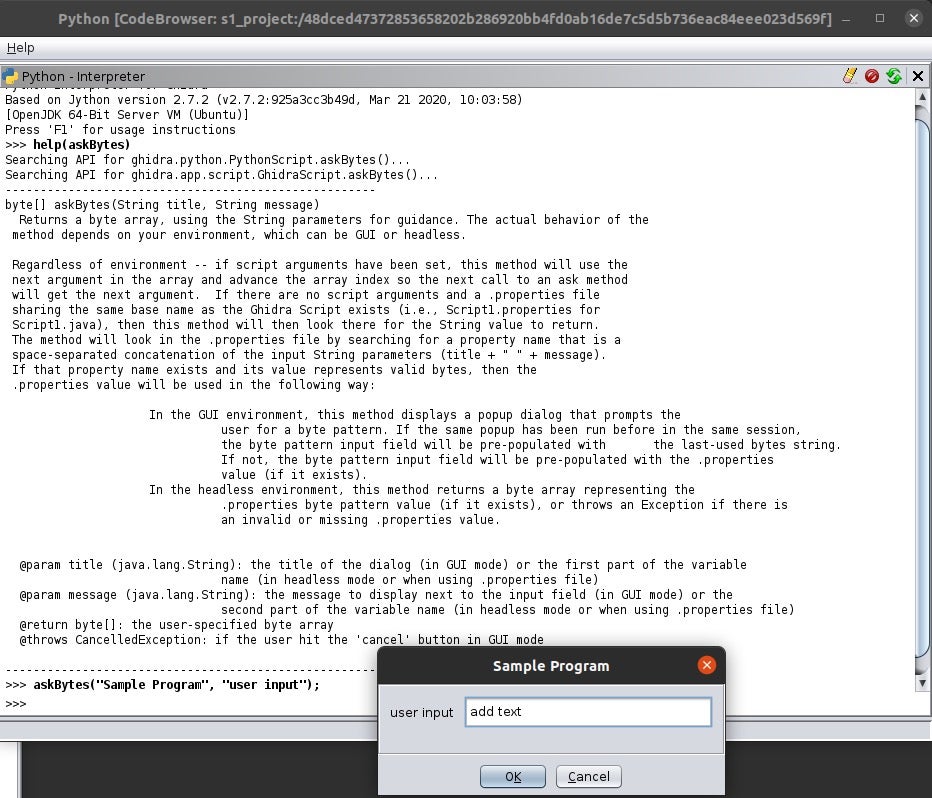
A Guide to Ghidra Scripting Development for Malware Researchers ...
Binary type inference in Ghidra - The Trail of Bits Blog
Extract disassembly from Ghidra for reassembling - Reverse Engineering ...
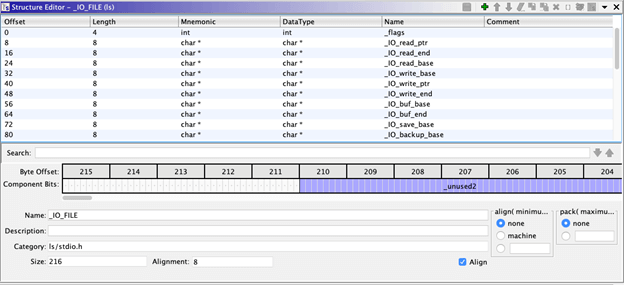
Ghidra 101: Creating Structures in Ghidra
Ghidra Plugin Development for Vulnerability Research - Part-1 ...
An Abstract Interpretation-Based Deobfuscation Plugin for Ghidra ...
Ghidra - Documentation
Ghidra 101: Creating Structures in Ghidra | Tripwire
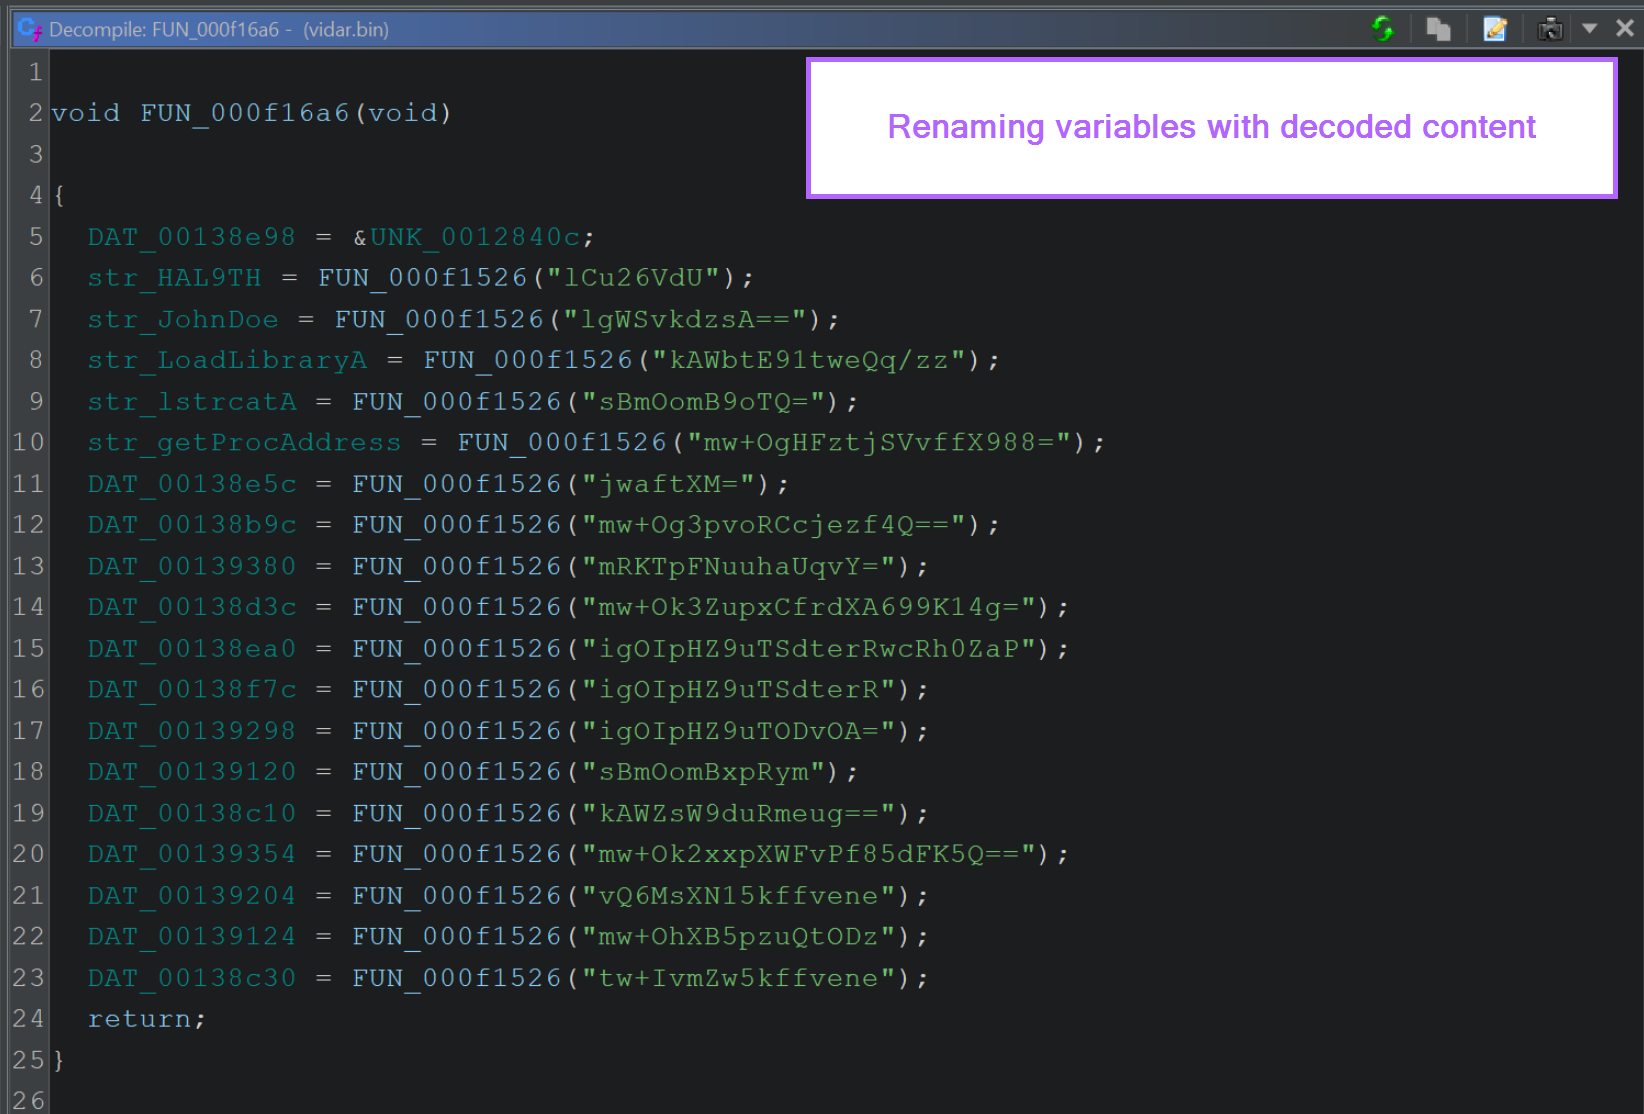
How To Use Ghidra For Malware Analysis - Identifying, Decoding and ...
How To Use Ghidra For Malware Analysis - Establishing Context on ...
Understanding and Improving The Ghidra UI for Malware Analysis
Reverse-engineering part 6: crash course on binary patching with Ghidra ...
Ghidra 10.2.3 keyboard shortcuts ‒ DefKey
Writing a GHIDRA Loader: STM32 Edition. | Wrongbaud's Blog
Reversing Cisco IOS Raw Binary Firmware Images with Ghidra · GitHub
Binary disassembly and decompilation howto using Ghidra · Issue #44 ...
ghidra-wasm-plugin Ghidra Wasm plugin with dis @codeKK AndroidOpen ...
Install Ghidra On Kali Linux | executeatwill
ghidra 使い方 – ghidra ダウンロード 方法 – EOHB
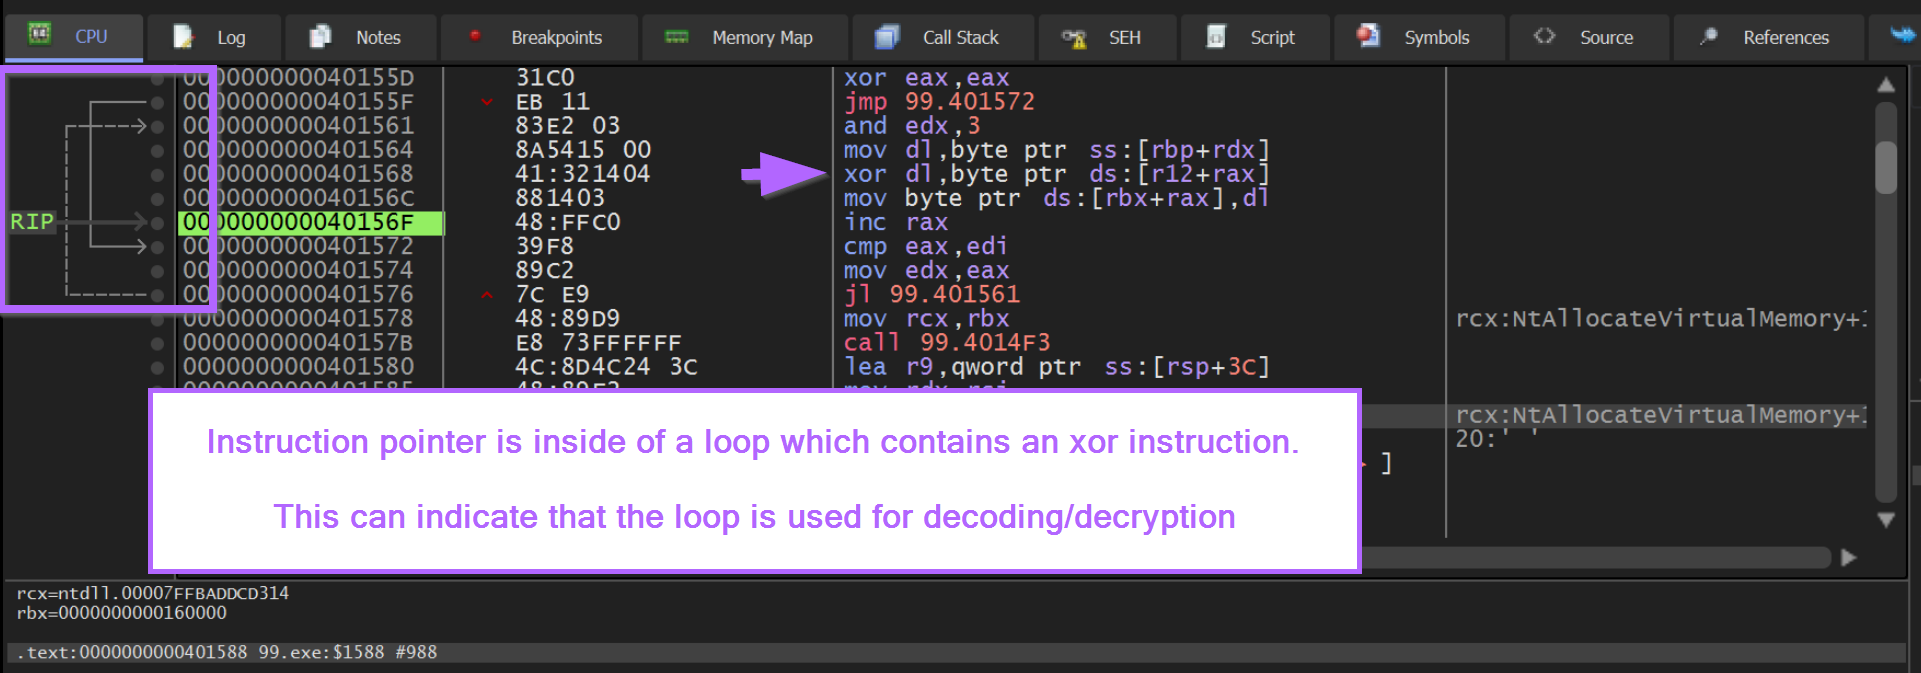
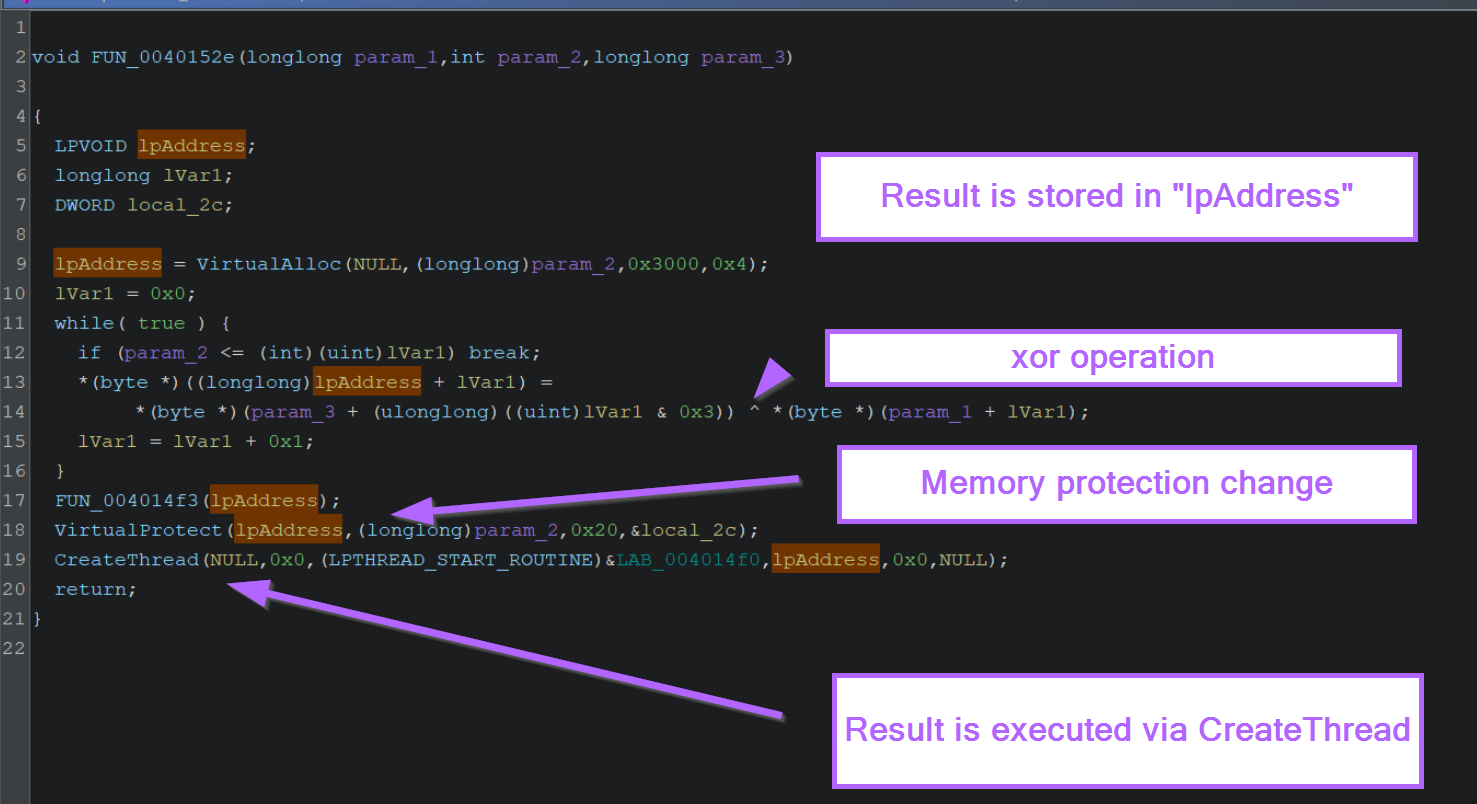
Beginner Ghidra Guide - Manual Shellcode Decryption
Ghidra Review 2026: NSA Reverse Engineering Tool
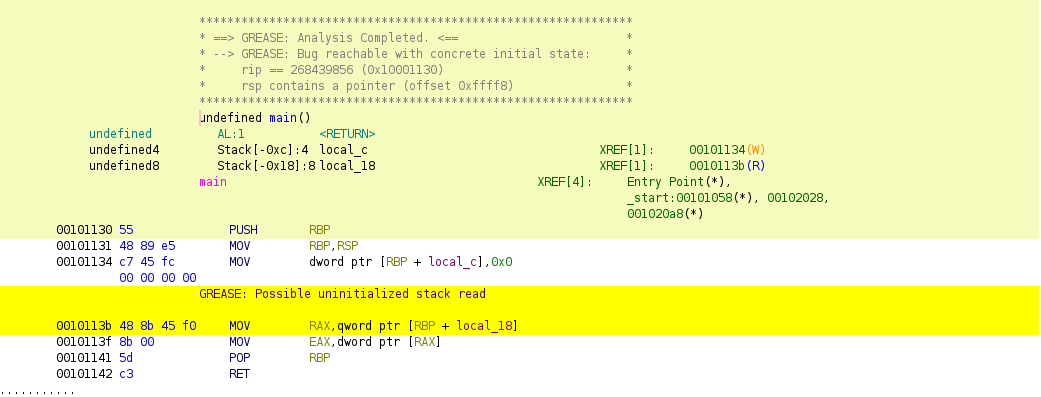
Ghidra plugin - GREASE
Implementing a brainfuck CPU in Ghidra - part 3: Decompilation of I/O ...
Introduction to Decompiling C++ with Ghidra - Retro Reversing (Reverse ...
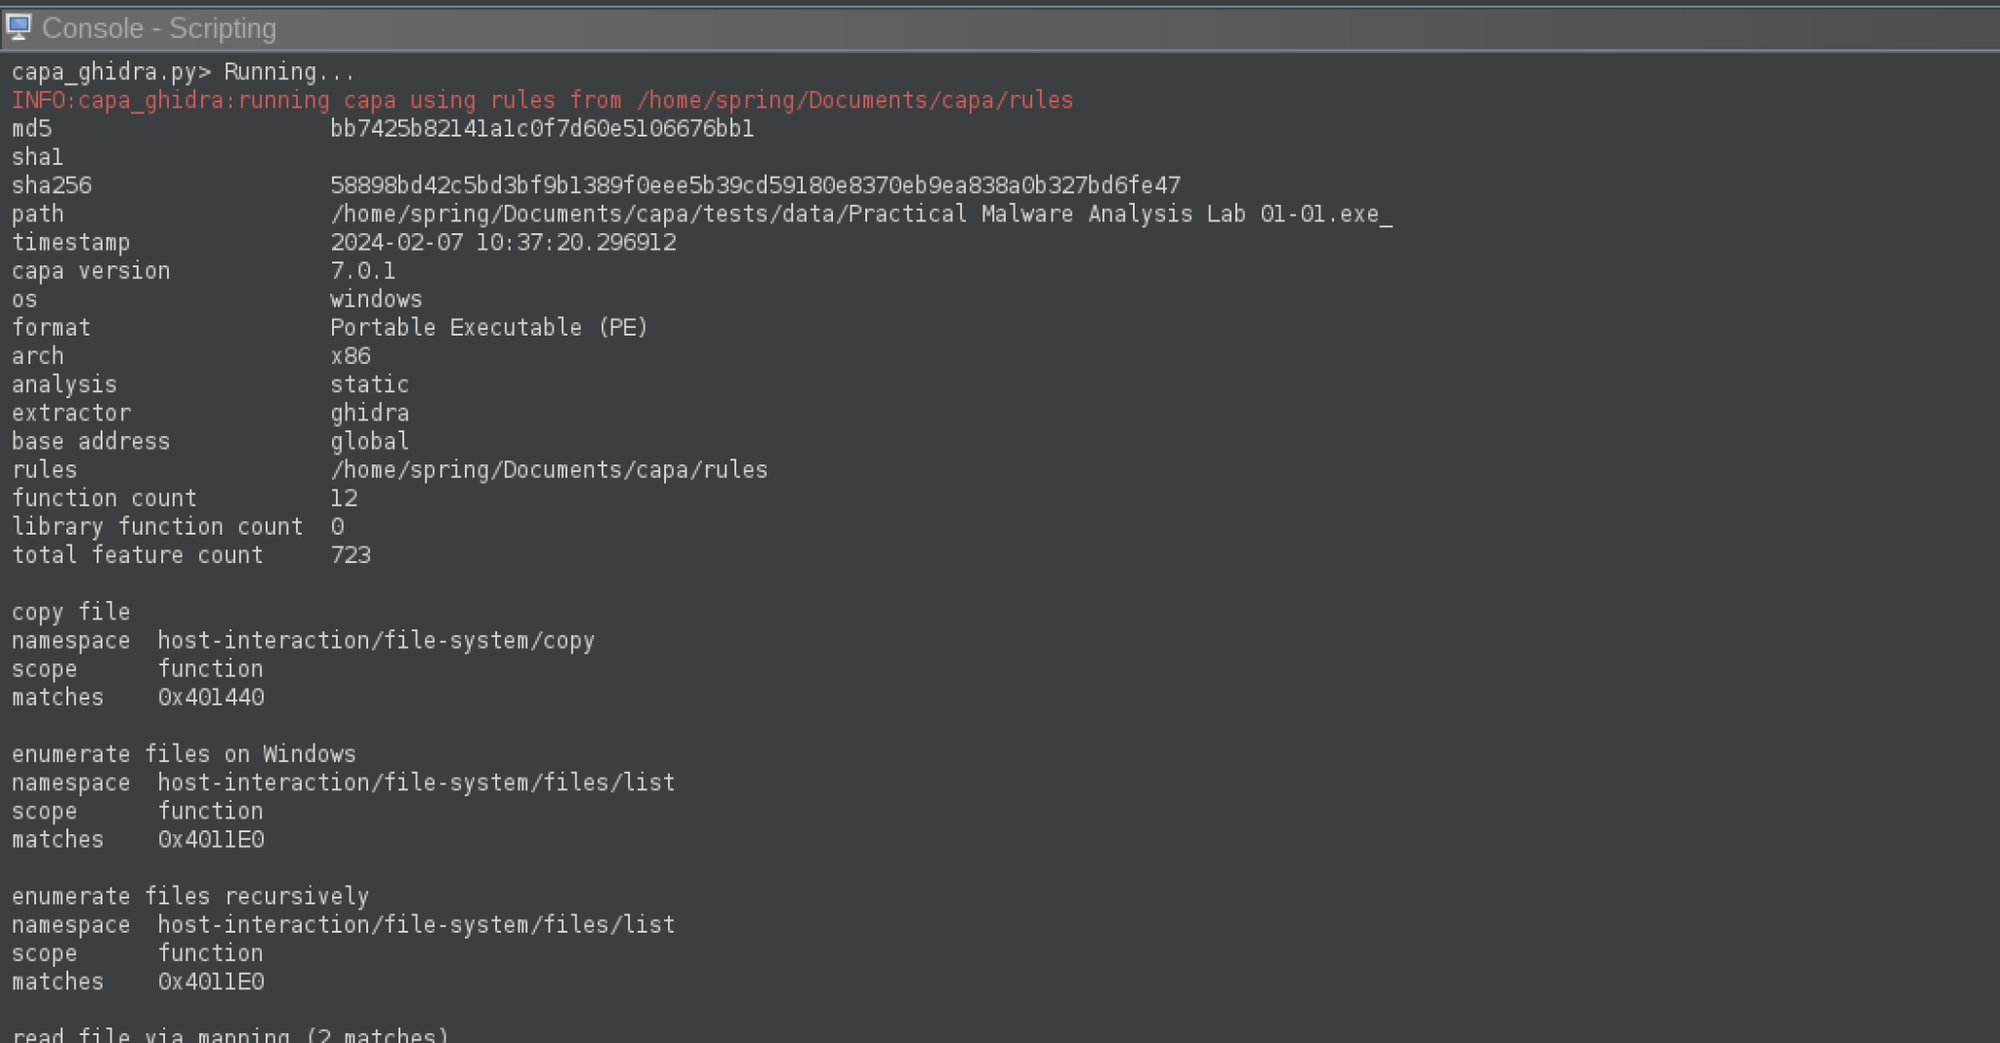
Riding Dragons: capa Harnesses Ghidra | Google Cloud Blog
How I Explain Ghidra Output With AI - DEV Community
Как приручить Ghidra | Securelist
Ghidra 安装与使用指南 | Blog
How to use Ghidra for malware analysis, reverse-engineering | TechTarget
Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec
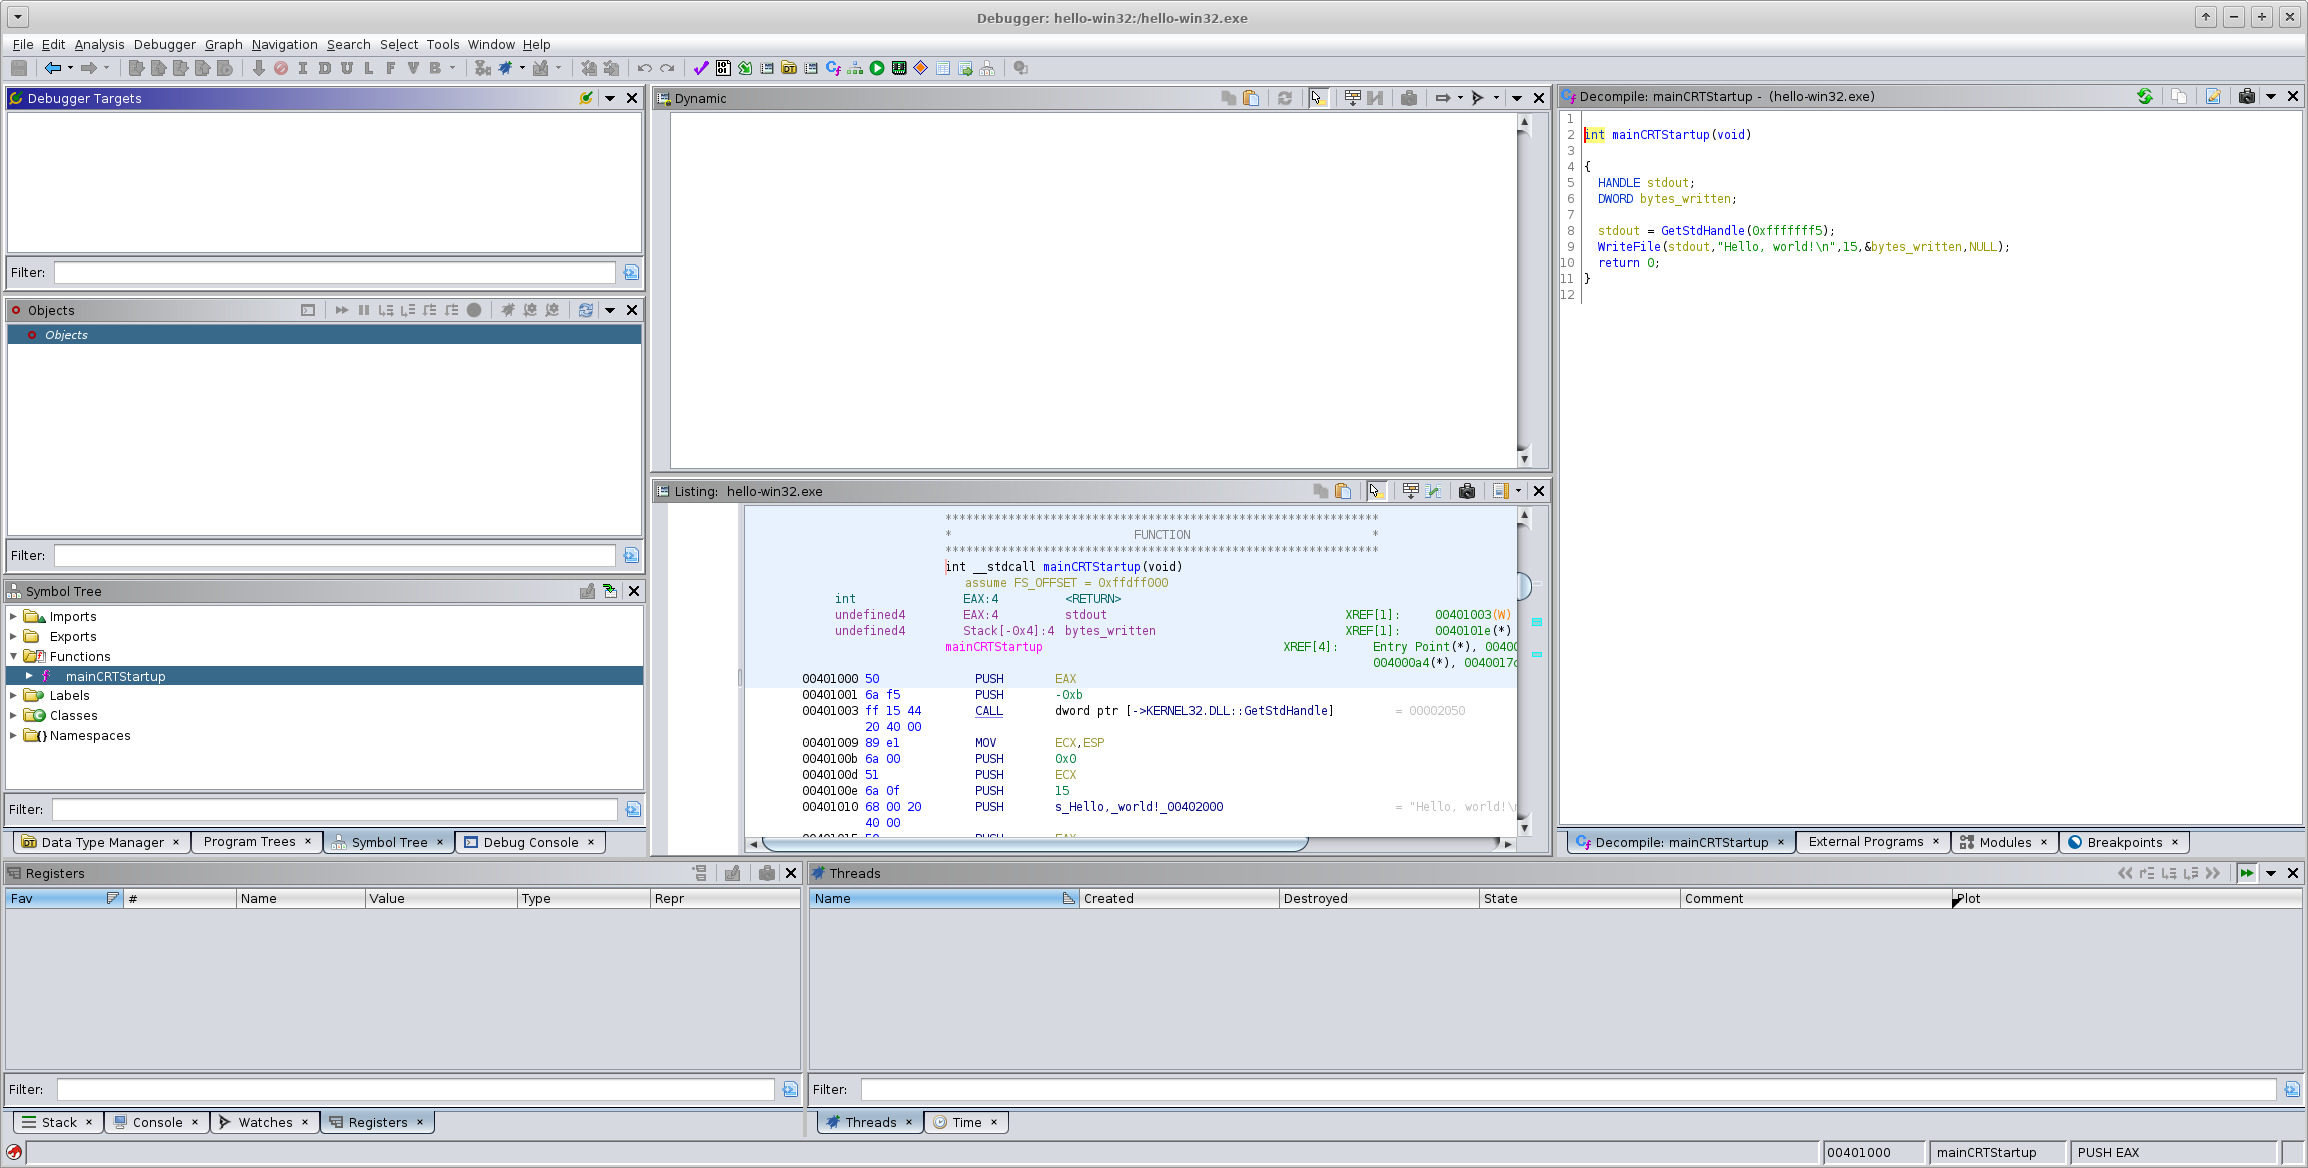
Debugging Win32 binaries in Ghidra via Wine
Day 14 - Ghidra - Headless Analyzer - CinCan
How to train your Ghidra
跟羽夏学 Ghidra ——初识 - 寂静的羽夏 - 博客园
Ghidra applies decompilation analysis even when disabaled · Issue #76 ...
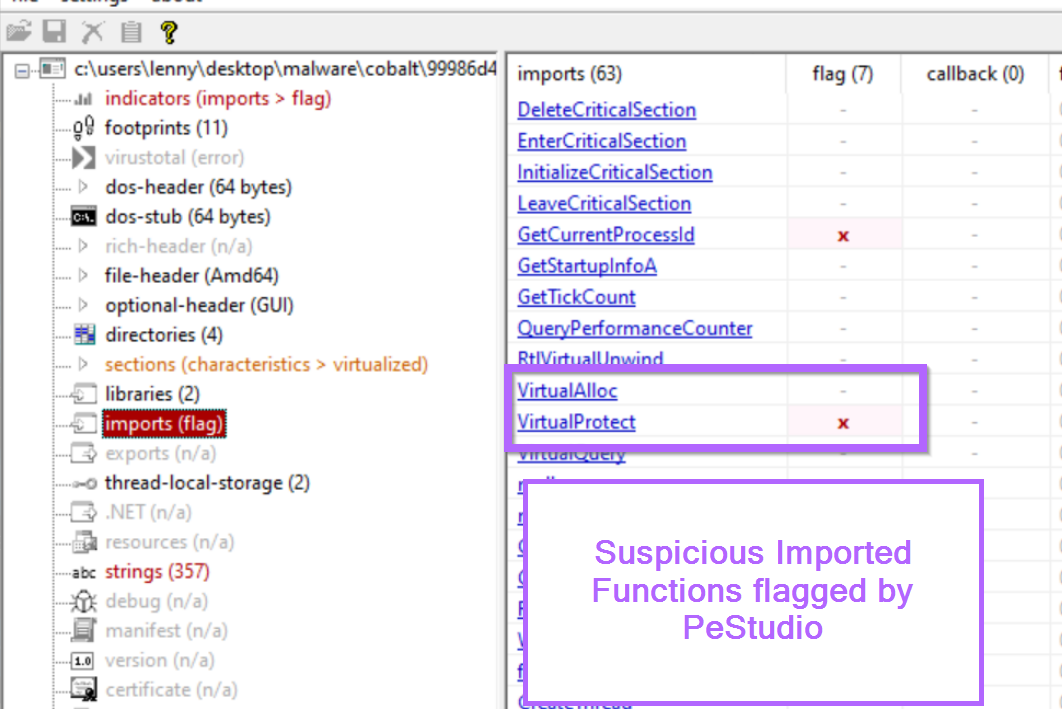
How to Use Ghidra to Reverse Engineer Malware | Varonis
Ghidra
First Look: Ghidra 10.3 Emulator. Ghidra 10.3 dropped this week with a ...
Ghidra :: purpole.io
disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...
What're you telling me, Ghidra? - byte.how
9 tools to help you reverse engineer games and more
CS6038/CS5138 Malware Analysis, UC by ckane
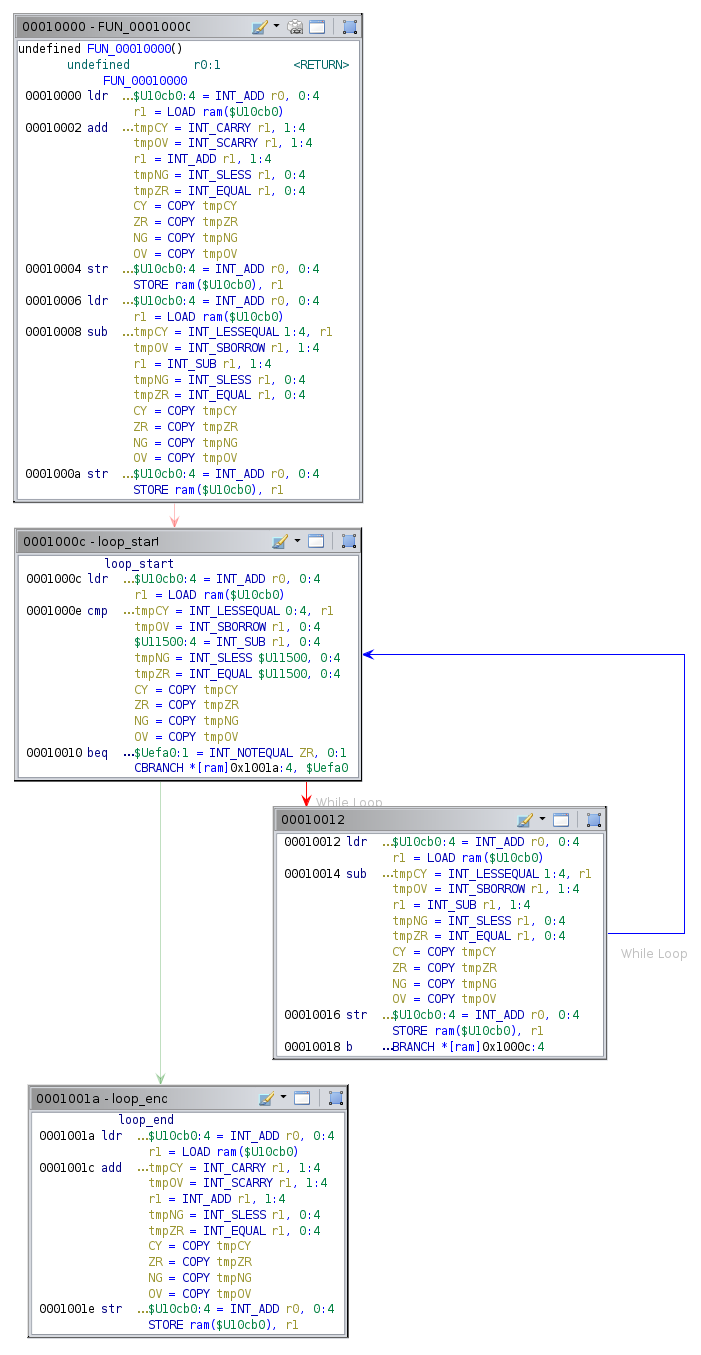
Reverse Engineering Loop Exercise :: 6rian's IT Blog
Internet of Things and Data Analytics
Reverse engineering: What is it and how to get started?
Here Be Monkeys | AVS Dev Blog
Firmware Reversing and Analysis Tools - Thyrasec
Ghidra: A quick overview for the curious | Shortjump!
Reverse Engineering a GBA Game - Starcube Labs - Gamedev Blog
Decompilación - Taller de Hacking Competitivo
Reverse Engineering a DS Game - Starcube Labs - Gamedev Blog
Introduction to Reverse Engineering with Ghidra: A Four Session Course ...
Comparision of Reverse-Engineering Tools | reHex Ninja
Different decompiler output after relocating image · Issue #3899 ...
Getting Started with Ghidra: Hands-On with the Powerful Reverse ...
Reverse Engineering
reverse engineering - Detecting symbols in arbitrary binary files ...
What Is Reverse Engineering in Cyber Security? [2026 Guide]
Chapter 2.1: Reverse Engineering - Geode Docs
display strings in the decompiler window? · Issue #4865 ...
disassembly - How to display the CFG of a function in Ghidra? - Reverse ...
7 open-source malware analysis tools you should try out - Help Net Security
Medium
Getting Started with Ghidra: Basic Binary Patching with String ...
lambdhack
はじめてのGhidra Debugger on Windows | Metarin's Blog
Is decompilation significantly more limited when performed on ...
Tutorial 2: Ripping, restoring, and decompiling the factory operating ...